Security for AI agents harnesses, SKILLs, MCPs, and plugins
Take control of your AI agent assets
Your teams install SKILLs, MCPs, and plugins faster than any review process can follow. Optimus Labs discovers each asset, maps what it can reach, inspects its posture, and watches what it does, alerting or blocking before a risky action leaves the machine.
Every install changes the code and the context an agent can touch. Optimus Labs tracks it continuously and breaks the combination across your agent assets before it breaks your security.
Four questions
Can your security team answer these today?
01
What is running?
Can you name the agents, MCP servers, SKILLs, and plugins in use today?
02
Where did it come from?
Can you trace publishers, repositories, updates, and configuration changes?
03
What can it reach?
Do you know which agents combine untrusted input, sensitive data, and external action?
04
What happens when it acts?
Can you spot anomalous behavior and block a risky tool call before it executes?
AI agents and assets Optimus Labs secures
Agent harnesses, SKILLs, MCP servers, plugins, hooks, and inference gateways





Lethal Trifecta makes every AI agent asset vulnerable
Named by Simon Willison, the Lethal Trifecta is the danger of an AI agent combining access to sensitive data, exposure to untrusted content, and a way to send data out.
When all three combine, one prompt injection can exfiltrate data or trigger unauthorized action. Optimus Labs breaks the combination across your agent assets before it breaks your security.
Lethal Trifecta coined by Simon Willison (opens in new tab).
From the field
What security leaders say
“As enterprises adopt AI agents, security teams need to understand and govern assets such as SKILLs, MCPs, and agent harnesses that can change, connect, and act across environments. Optimus Labs is focused on that challenge, with a security layer designed for the way agents operate.”
Threat research
Original research, published in the open
We investigate real attacks on AI agent assets, publish the evidence, and release the tools we build to investigate them.
Open-source incident response
GrokPatrol
Find out whether Grok Build CLI collected and queued your repositories for upload, including secrets deleted from the working tree but still present in Git history.
Investigate your exposureThe team
The people behind Optimus Labs
Backed by


Why this matters now
Agents are moving into enterprise workflows faster than the controls needed to govern their access and actions.
82%
of organizations discovered AI agents or workflows that security or IT previously didn't know about in the past year.
Unknown agents are the norm, not the exception.
Cloud Security Alliance, April 20261,708
credential-leakage issues found across 17,022 analyzed agent SKILLs.
Bundled SKILLs leak live tokens and keys straight from public repositories.
Academic research, June 2026150K+
agents forecast in the average Fortune 500 enterprise by 2028. Only 13% believe their governance is suited to that scale.
Agent sprawl is coming whether security teams are ready or not.
Gartner, April 2026Complete your security stack
EDR watches processes. AppSec watches pipelines. Both read agent asset activity as innocuous user behavior. Optimus Labs watches the new, dynamic attack surface that AI agent assets create.
EDR
Processes
Monitors endpoints
AppSec
Pipelines
Monitors DevSecOps workflows
Optimus Labs
Agent assets
Watches the attack surface others miss
Watches what each asset does and enforces at runtime
What Optimus Labs does
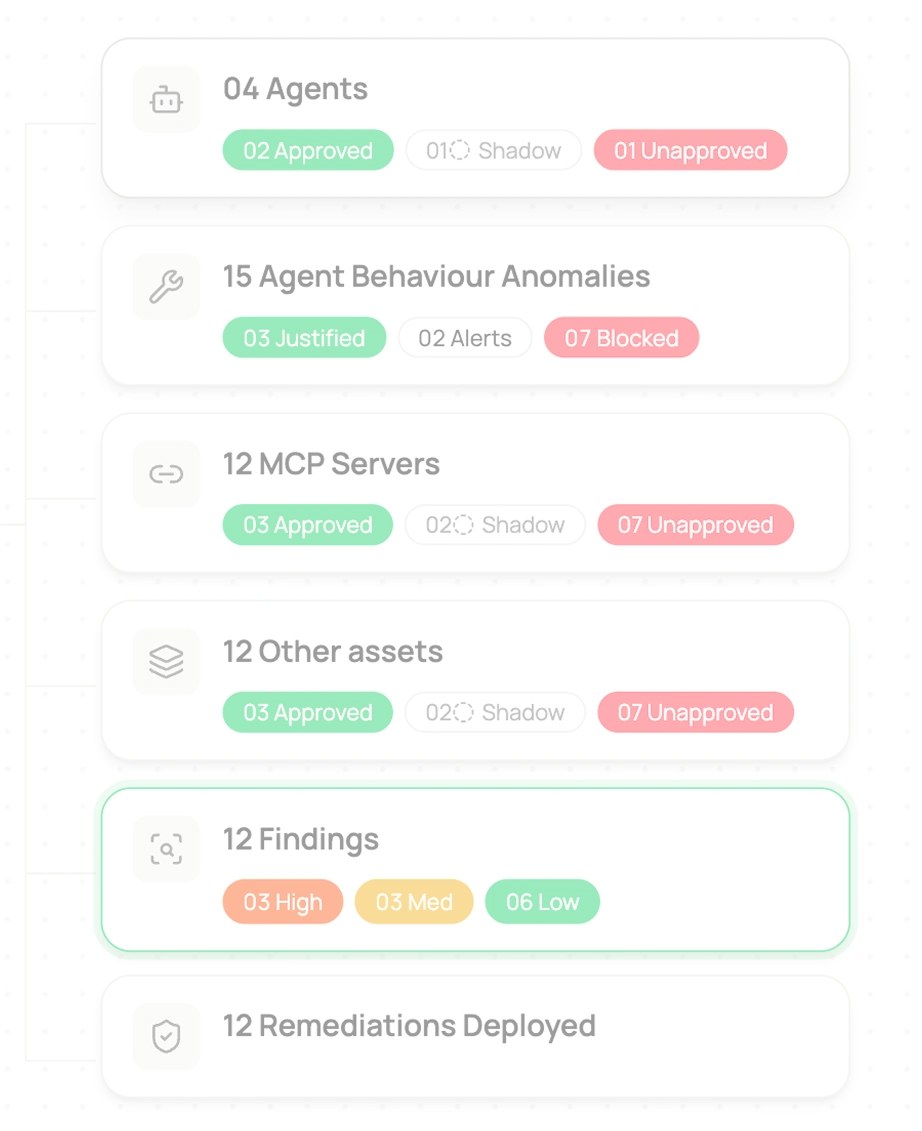
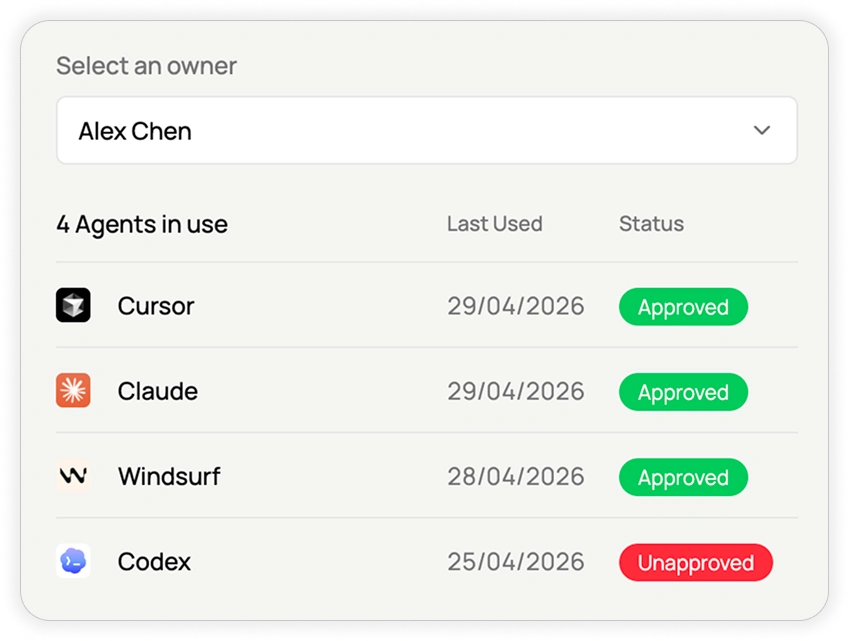
From the moment an agent is installed to the moment it acts, one sensor on the endpoint.
Integrations
Fits the stack you already run
Deploys through your MDM, ties every asset to your identity provider, and sends detections to the tools your team already watches. Prompts and file contents stay on your devices by default. Optimus Labs receives only AI agent asset and behaviour metadata, never PII.
Deploys through
- Every MDM
- Jamf Pro
- Microsoft Intune
MDM integrations unlock a richer featureset for governance and control.
Agentic security operations
- Optimus Labs MCP
Security teams run agentic security operations from the AI assistants they already use. We meet your team where it works.
Identity and owners
- Okta
- Microsoft Entra ID
Agent ecosystem
- Claude Compliance API
- Claude Connector and Plugin
- AWS
Code and supply chain
- GitHub
- GitLab
- Snyk
- Aikido
Tie agent assets to the dependency and code scans your teams already run.
Alerts and telemetry where teams work
- Slack
- Microsoft Teams
- Webhooks
- Splunk
- Datadog
- Coralogix
Ticketing and workflows
- Linear
- Jira
Threat intelligence
- MISP
- OpenCTI
- VirusTotal
- Recorded Future
Detections enrich with the indicators and intel feeds your team already trusts.
Vulnerability intelligence
- OSV
- NVD
- GitHub Advisory Database
- CISA KEV
Every asset is matched against these feeds. Optimus Labs also flags exposures that never received a CVE.
AI supply chain security
Supply chain risk does not end at the package scan
A trusted SKILL can be hijacked after review. A plugin update can change what it does. An MCP server configuration can grant excess access. Untrusted input can steer a legitimate tool. Optimus Labs connects the provenance and posture of every agent asset to what the agent later attempts.
Find every agent asset, score its risk, enforce at runtime
A lightweight, agentless sensor protects agent assets wherever they run, with deep endpoint coverage where most enterprise agent assets execute. Install the sensor, review the inventory, turn on policies.
Connect
Deploys through your MDM in minutes. macOS and Windows today, Linux coming soon. The lightweight sensor does not continuously consume compute. No code changes, no proxy, nothing added to the request path.
Discover
Surface the SKILLs, MCP servers, plugins, hooks, and inference gateways your teams run, across managed endpoints and cloud VMs, and tie every asset to the identity and owner behind it.
Enforce
Score each asset's posture, watch its behavior for anomalies, and alert or block before the action takes effect.
Questions we hear most
Break the Lethal Trifecta before it breaks your security
See every agent asset, what it can reach, and the risky combinations, then enforce policy before the action takes effect.