Security for AI agent harnesses, SKILLs, MCPs and plugins
Take control of your AI agent assets
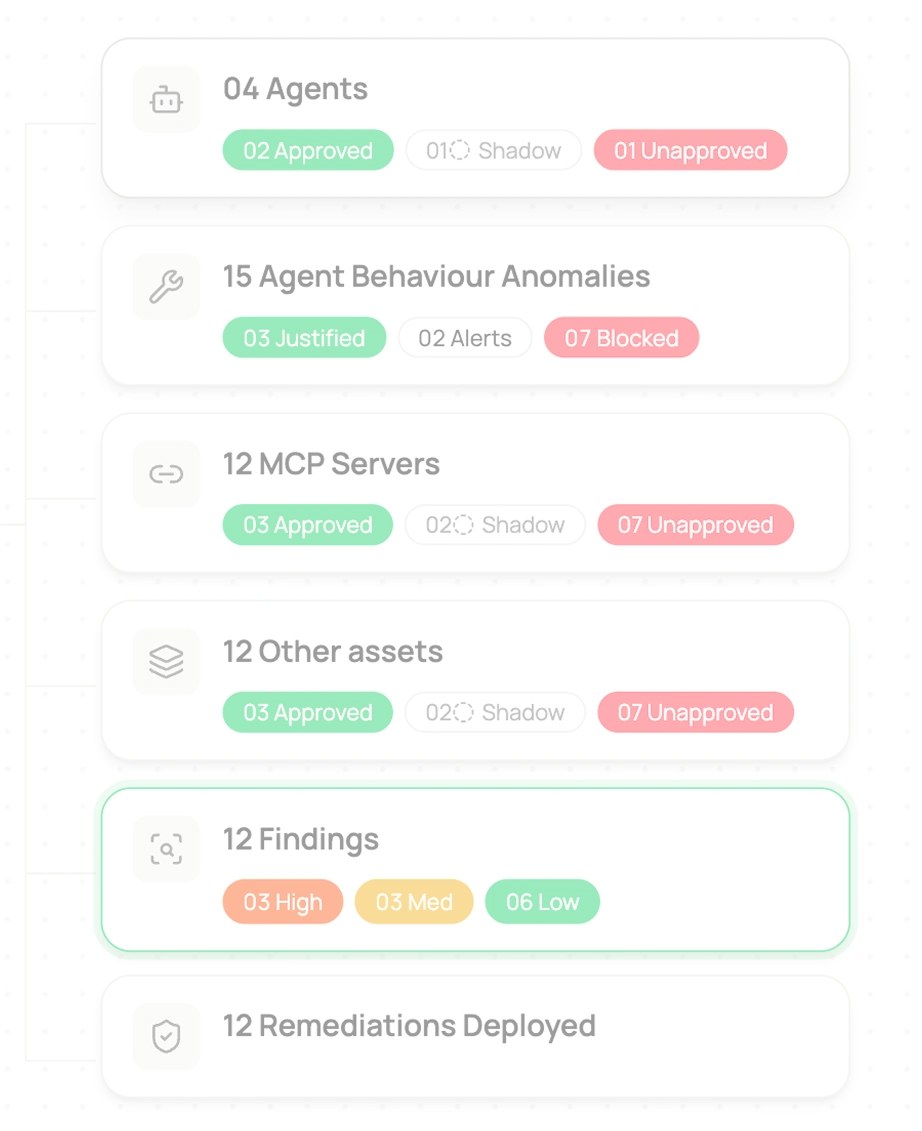
Optimus Labs delivers secure paved paths for AI agent assets used across your enterprise. We discover and map your agent attack surface, inspects its posture and intent, and detect and block a risky action before it impacts your enterprise.
AI agents and assets Optimus Labs secures
Agent harnesses, SKILLs, MCP servers, plugins, hooks, and inference gateways
 SKILLs


 MCP






 SKILLsMCP
Five questions
Can you answer these about AI powering your enterprise?
01
What is running?
Can you name the agents, MCP servers, SKILLs, and plugins in use today?
02
Where did it come from?
Can you trace assets, repositories, updates, and configuration changes done by Agents?
03
What can it reach?
Do you know which agents combine untrusted input, sensitive data, and external action?
04
What happens when it acts?
Can you spot anomalous behaviour and block a risky tool call before it executes?
05
Can you stop it now?
Does your security team, or your users, have an agent kill switch to enforce a permission or behaviour?
The Lethal Trifecta turns one prompt into a breach
Named by Simon Willison, the Lethal Trifecta is the danger of an AI agent combining access to sensitive data, exposure to untrusted content, and a way to send data out.
When all three combine, one prompt injection can exfiltrate data or trigger unauthorized action. Optimus Labs finds the agents that hold all three and blocks the action that completes the chain.
Lethal Trifecta coined by Simon Willison (opens in new tab).
What Optimus Labs does
From the moment an agent is installed to the moment it acts, with deep endpoint coverage wherever agents run.
From the field
What security leaders say

“As enterprises adopt AI agents, security teams need to understand and govern assets such as SKILLs, MCPs, and agent harnesses that can change, connect, and act across environments. Optimus Labs is focused on that challenge, with a security layer designed for the way agents operate.”




AI agent asset supply chain
Supply chain risk does not end at the package scan
A trusted SKILL can be hijacked after review. A plugin update can change what it does. An MCP server configuration can grant excess access. Untrusted input can steer a legitimate tool. Optimus Labs connects the provenance and posture of every agent asset to what the agent later attempts.
Why this matters now
Agents are moving into enterprise workflows faster than the controls needed to govern their access and actions. Figures below are from published research, as of October 2026.
82%
of organizations discovered AI agents or workflows that security or IT previously didn't know about in the past year.
Unknown agents are the norm, not the exception.
Cloud Security Alliance, April 20261,708
credential-leakage issues found across 17,022 analyzed agent SKILLs.
Bundled SKILLs leak live tokens and keys straight from public repositories.
Academic research, June 2026150K+
agents forecast in the average Fortune 500 enterprise by 2028. Only 13% believe their governance is suited to that scale.
Agent sprawl is coming whether security teams are ready or not.
Gartner, April 202647%
of CISOs saw AI agents behave in unintended or unauthorized ways in enterprise environments.
33% experienced an AI-related incident or near-miss.
Saviynt CISO AI Risk Report, 2026Threat research
Original research, published in the open
We investigate real attacks on AI agent assets, publish the evidence, and release the tools we build to investigate them.
Open-source incident response
GrokPatrol
Find out whether Grok Build CLI collected and queued your repositories for upload, including secrets deleted from the working tree but still present in Git history.
Investigate your exposureHow you deploy
A lightweight, agentless sensor protects agent assets wherever they run, with deep endpoint coverage where most enterprise agent assets execute. Install the sensor, review the inventory, turn on policies.
Connect
Deploys through your MDM in minutes. macOS, Windows and Linux. The lightweight sensor does not continuously consume compute. No code changes, no proxy, nothing added to the request path.
Discover
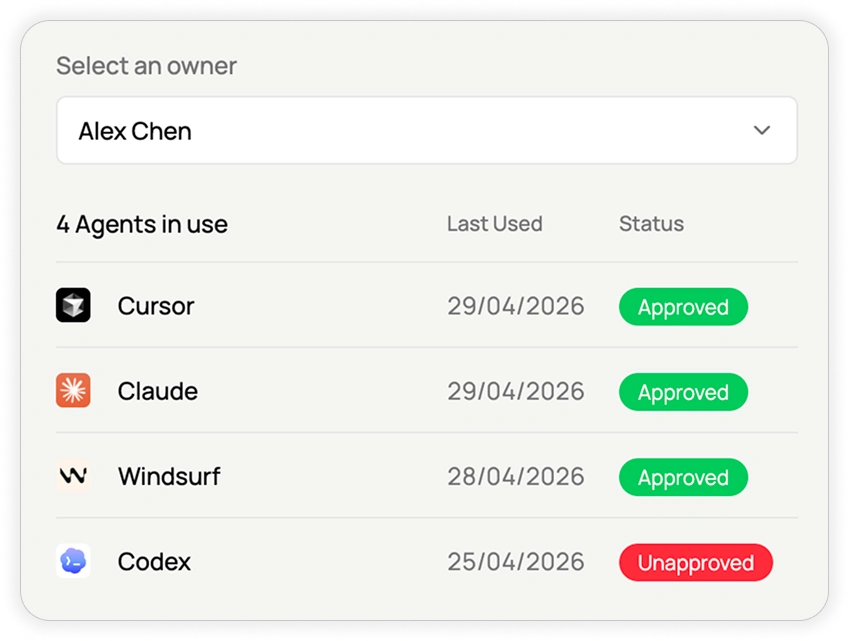
Review the inventory: every harness, SKILL, MCP and plugin your teams run, across managed endpoints and cloud VMs, tied to the identity and owner behind it.
Enforce
Turn on policies: fix posture, watch Behaviour for anomalies, and alert or block before the action takes effect.
Complete your security stack
EDR watches processes. AppSec watches pipelines. Both read agent asset activity as innocuous user Behaviour. Optimus Labs watches the new, dynamic attack surface that AI agent assets create.
EDR
Processes
Monitors endpoints
AppSec
Pipelines
Monitors DevSecOps workflows
Optimus Labs
Agent assets
Watches the attack surface others miss
Inspects each asset and enforces policy at runtime
Built to assist your team with secure outcomes
Your team keeps working as before.
They use their agents exactly as they do today, with nothing new to sign in to, approve or click.
Your team never waits on Optimus.
If the console can't be reached, or a policy check can't run, the action goes through, the activity is saved and sent later, and security is told.
Your team hears from Optimus only when you decide.
When a policy stops a risky action, they see a short message explaining why. If your policy allows it, they can use the kill switch on their own agents too.
The team
The people behind Optimus Labs
Backed by

Questions we hear most
Break the Lethal Trifecta before it breaks your security
See every agent asset, what it can reach, and the risky combinations, then enforce policy before the action takes effect.